Topic
AI Security
9 stories on this topic, newest first.
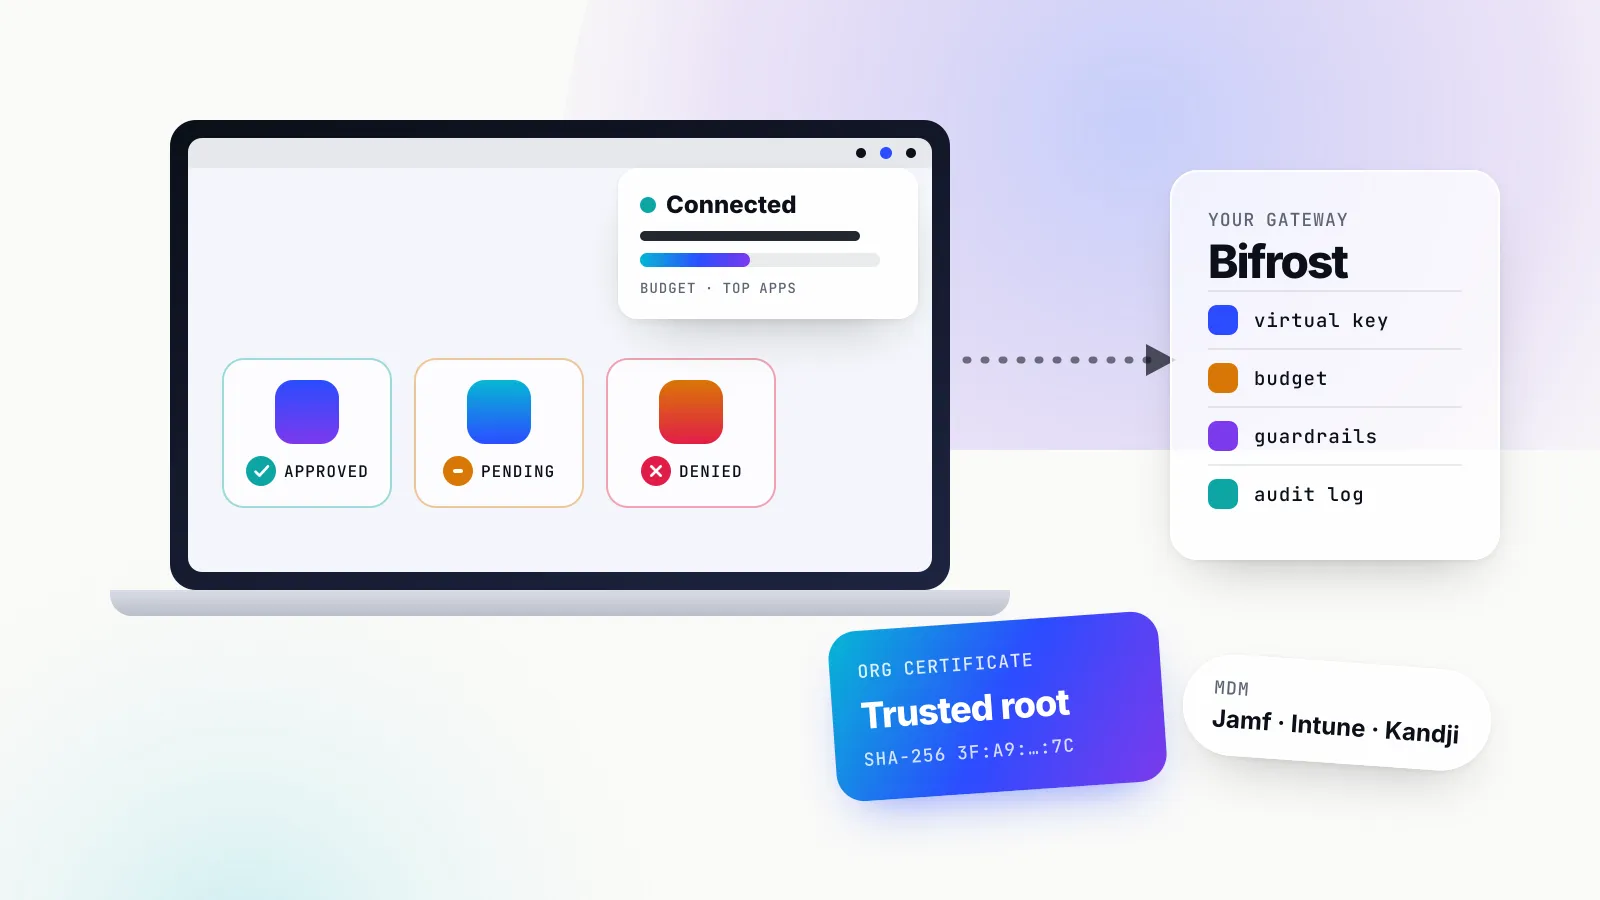
Bifrost Edge moves the AI gateway from the data centre onto every laptop
Maxim AI's Bifrost Edge is an endpoint agent that routes desktop chat apps, browser AI, coding agents and MCP servers through the company gateway, with app and MCP approvals, guardrails and MDM rollout.
ToolsExplainer
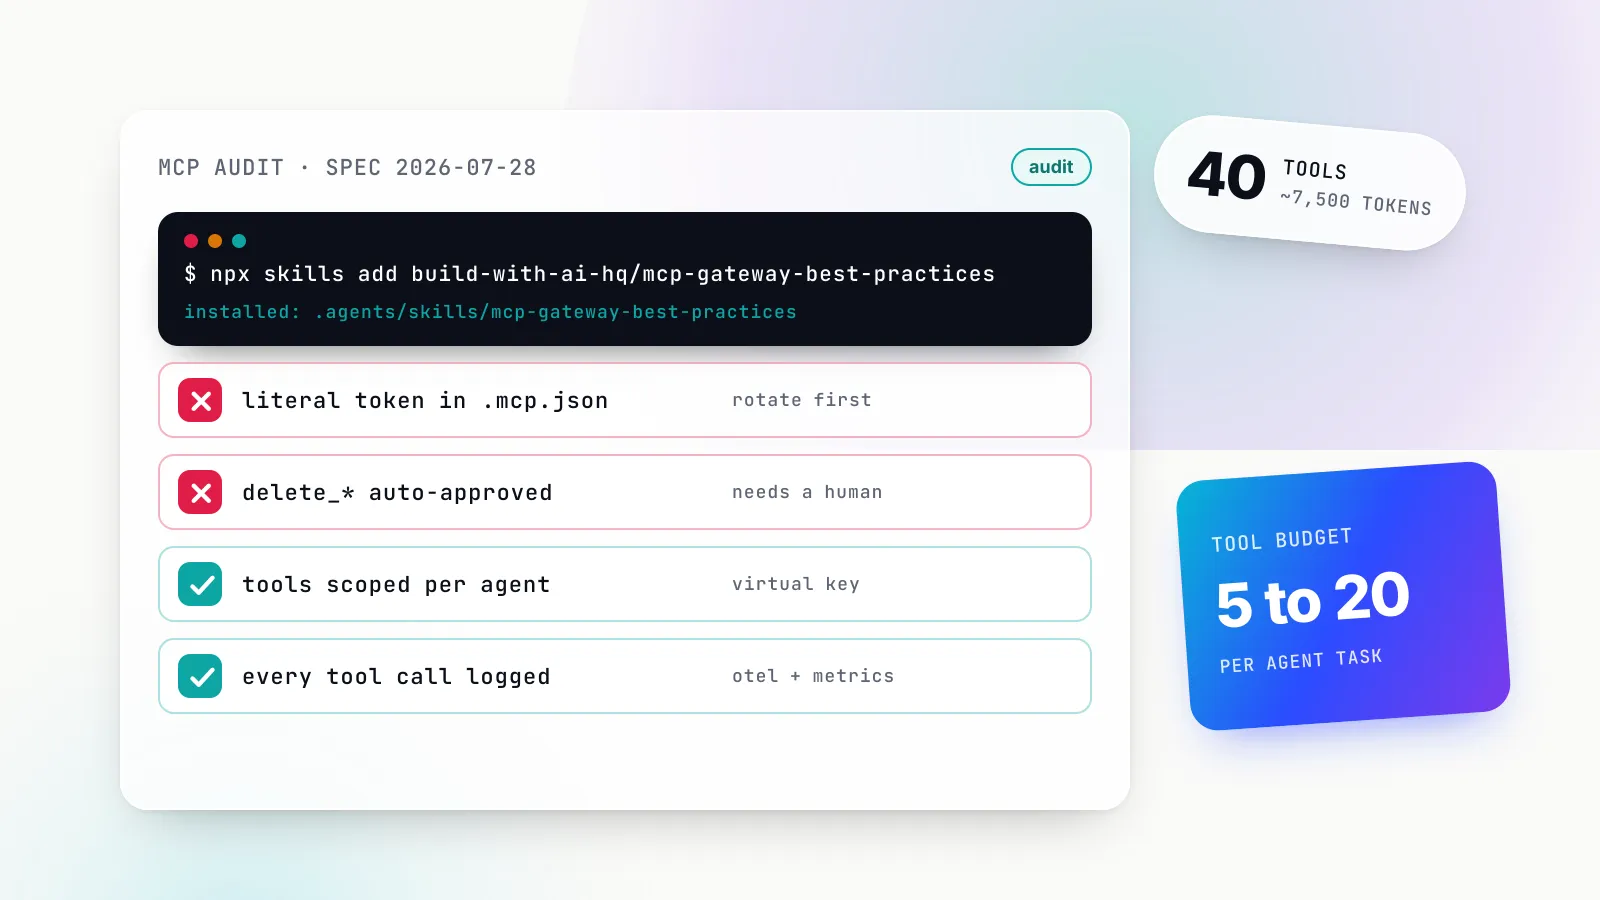
MCP best practices: tool budgets, permissions and approvals for real agent teams
Ten MCP best practices for the 2026-07-28 spec, each with a bad and good example and a check: tool budgets, naming, least privilege, approvals, transports, logs and tests.
ToolsExplainer
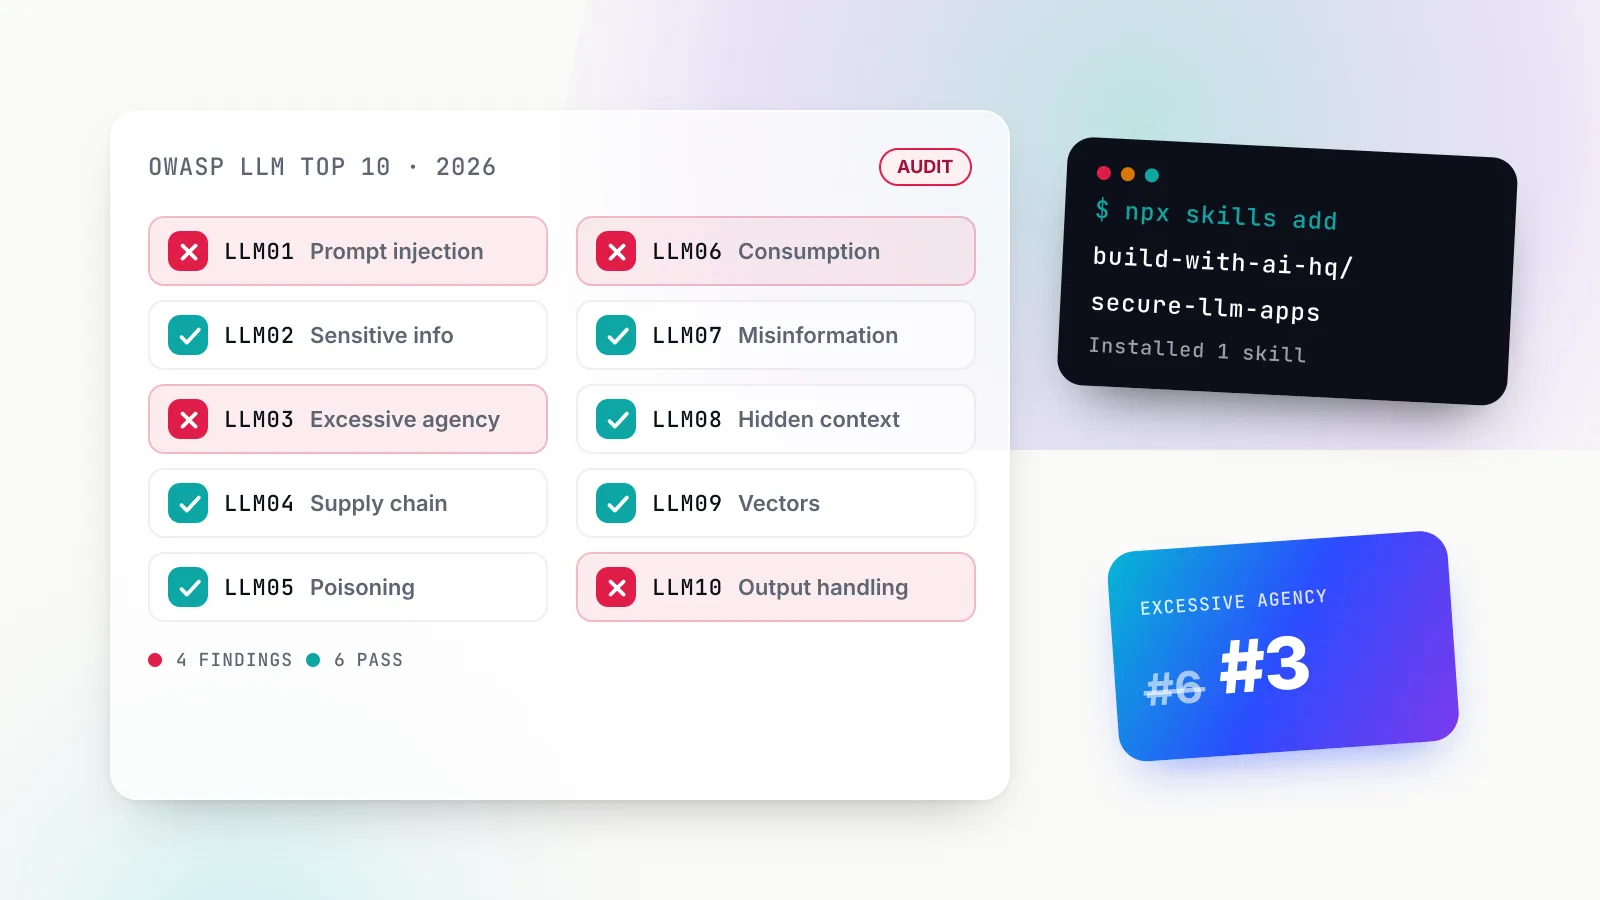
OWASP LLM Top 10 (2026): every risk, the vulnerable code and the fix
The 2026 OWASP LLM Top 10 reorders the list and renames one entry. Each risk with a vulnerable pattern, the Python or TypeScript fix, and an LLM security checklist.
ToolsExplainer
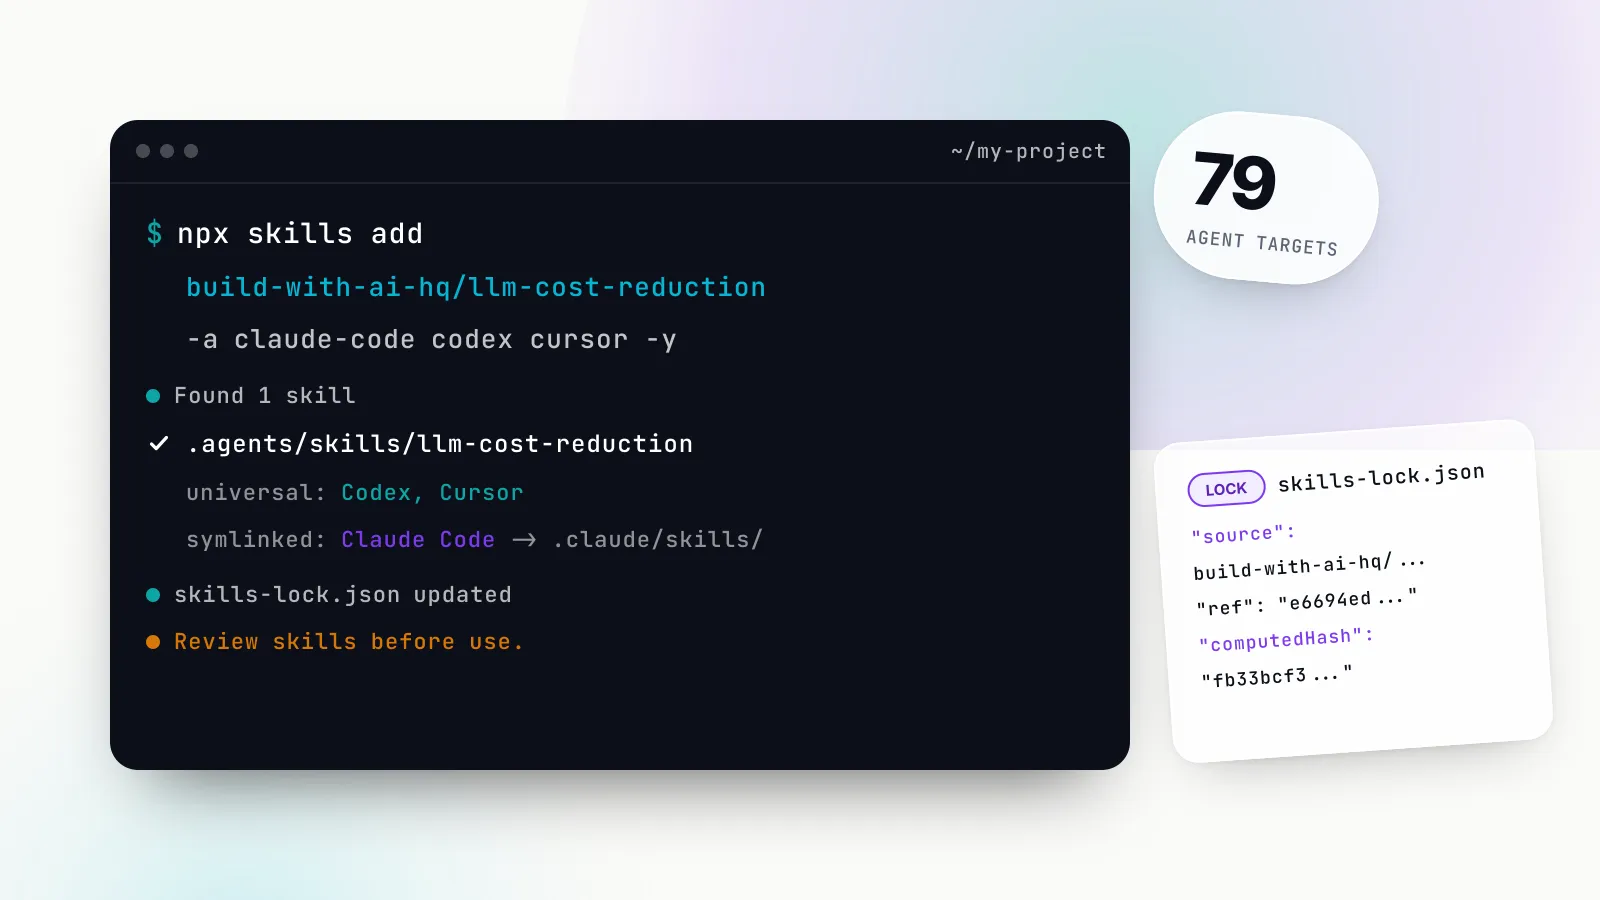
skills.sh and npx skills add: the complete guide to installing agent skills
What skills.sh is, who runs it, and every skills CLI command tested: how npx skills add resolves repos, scope, agent targeting, symlinks, skills-lock.json, telemetry and security review.
ToolsExplainer
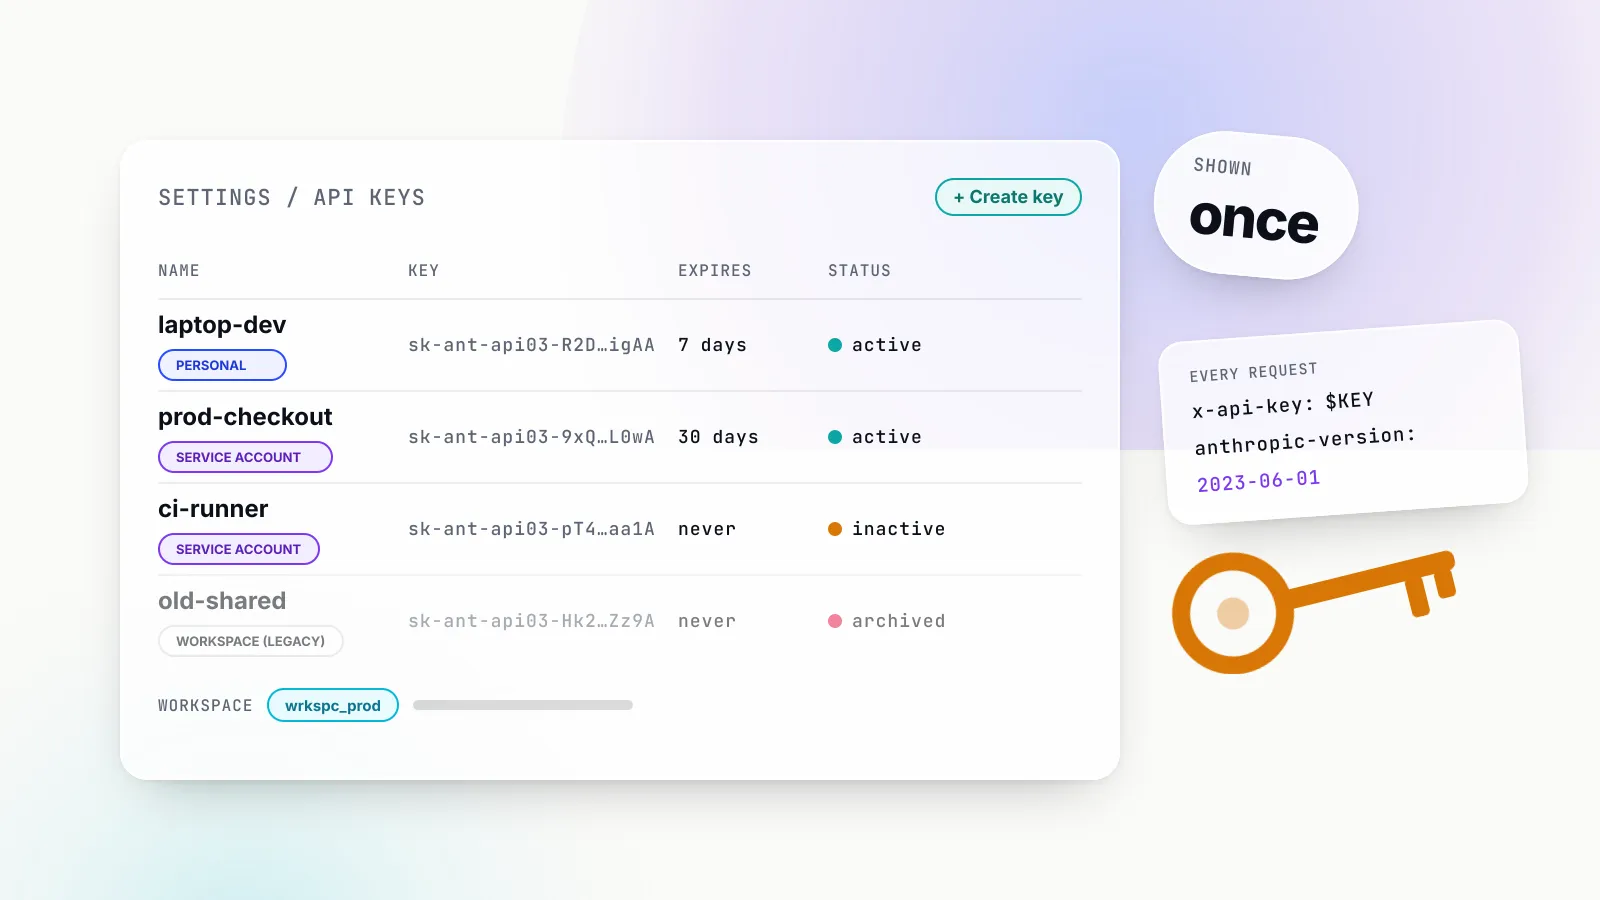
Claude API keys: how to create, scope, secure and rotate them
A Claude API key is a sk-ant secret from the Claude Console. Key types, workspaces, headers, limits, expiry, leaks, Claude Code precedence and cloud auth, as of October 2026.
ToolsExplainer
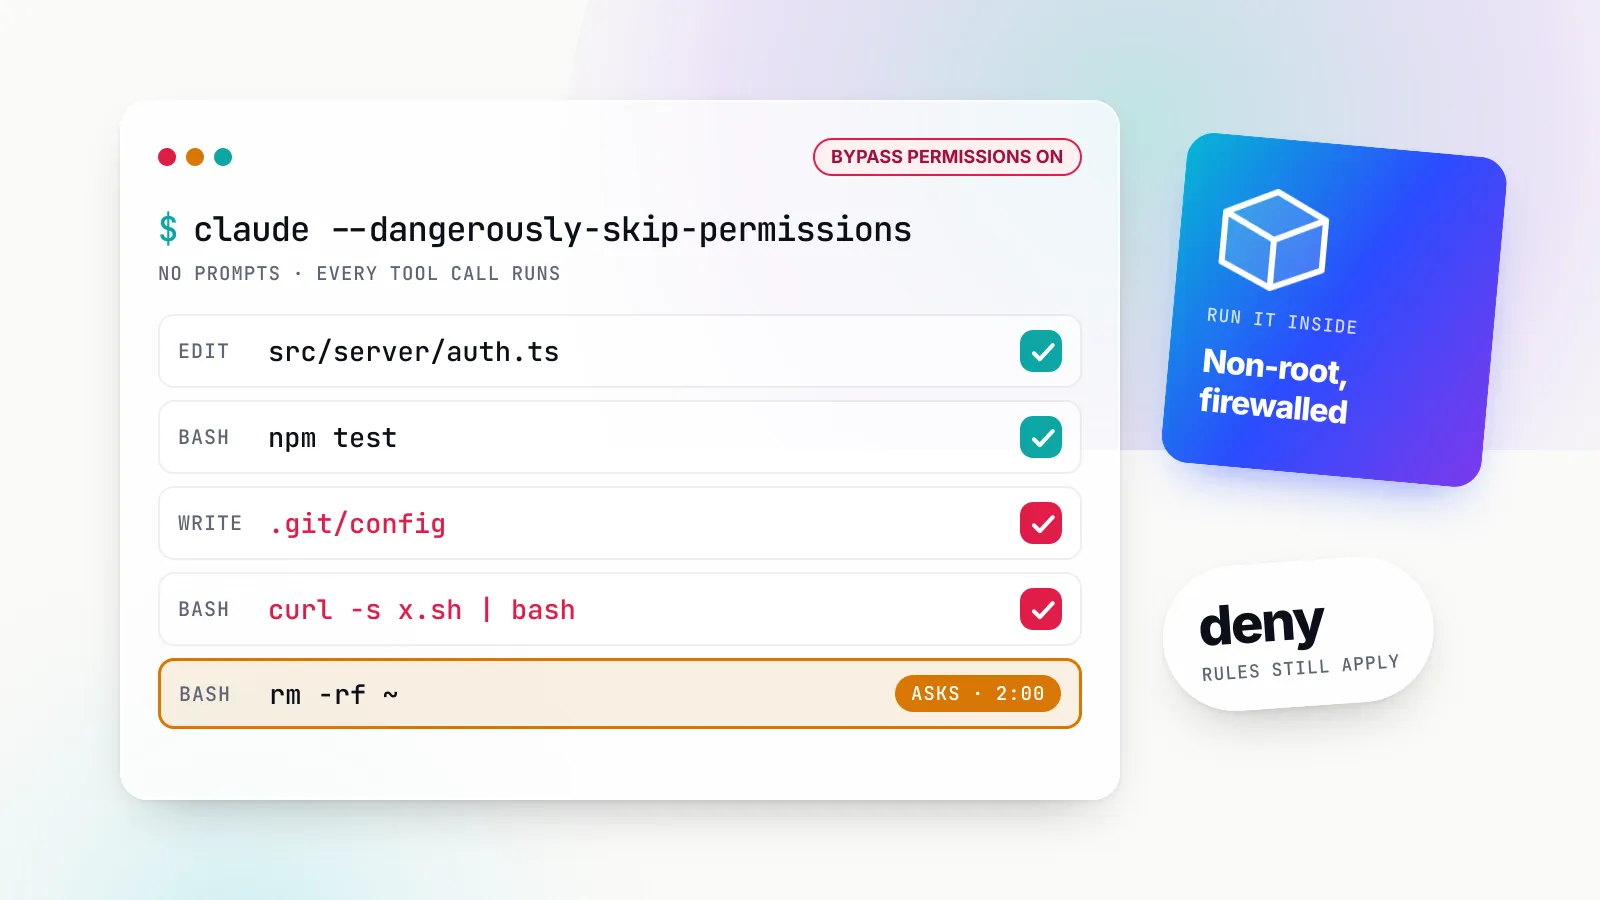
Claude --dangerously-skip-permissions: a practical guide to what it bypasses
What Claude Code's --dangerously-skip-permissions flag skips, the checks that survive it, real incident patterns, and safe recipes for containers, sandboxes and CI.
ToolsExplainer
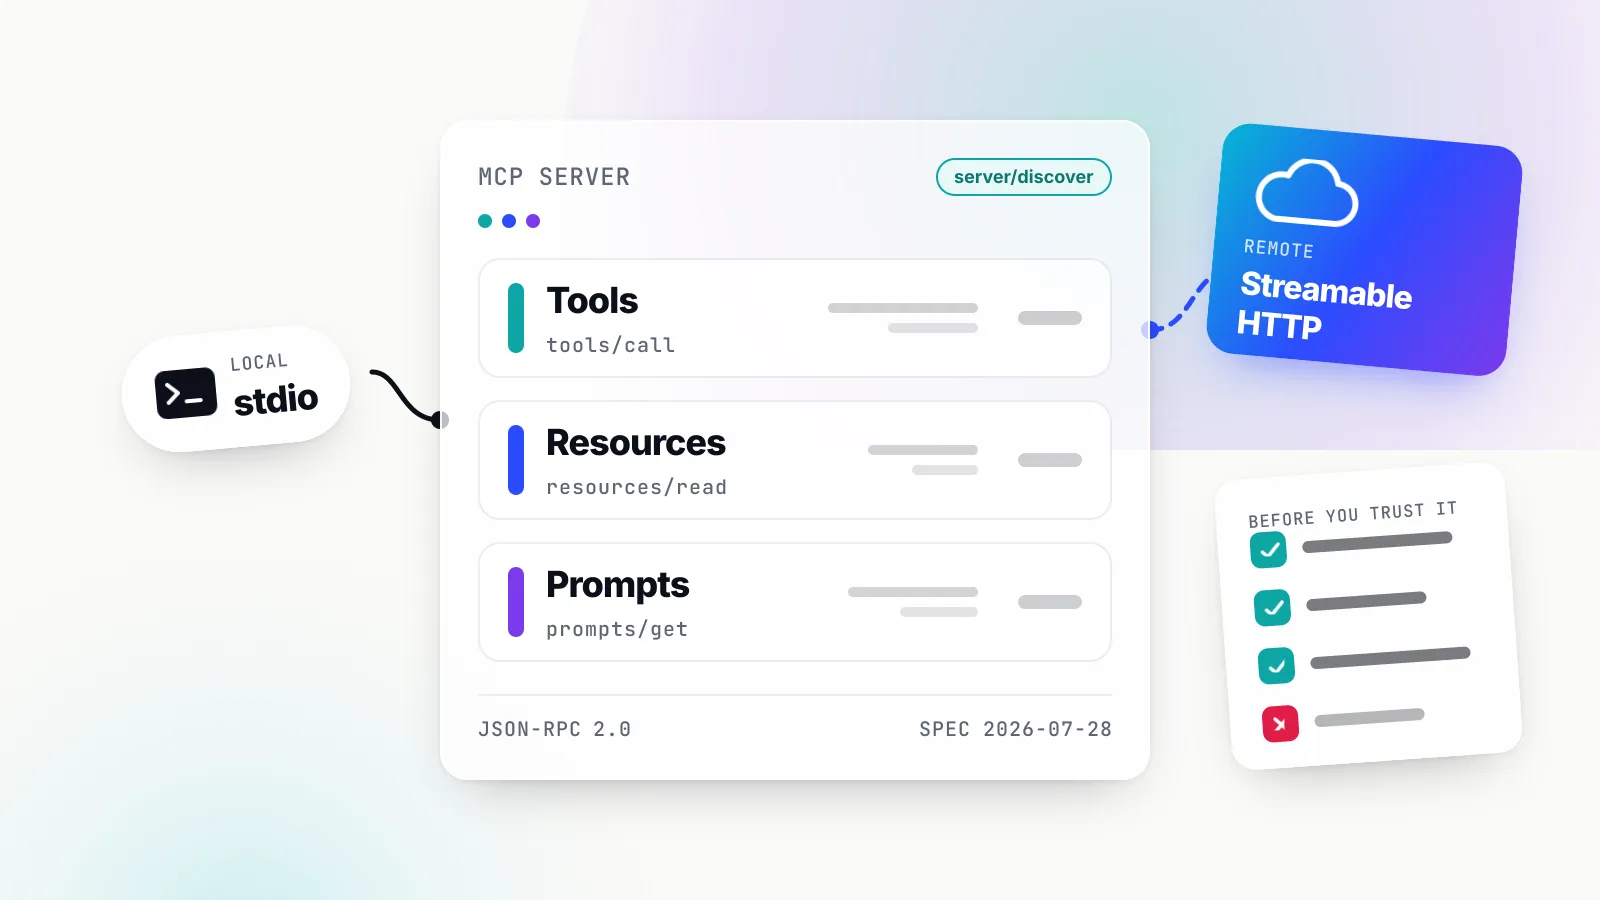
What is an MCP server? Meaning, anatomy and how to vet one
An MCP server is the program that hands an AI app its tools, resources and prompts. What it is and is not, stdio versus HTTP, a working server in TypeScript and Python, and the trust checks.
ToolsExplainer
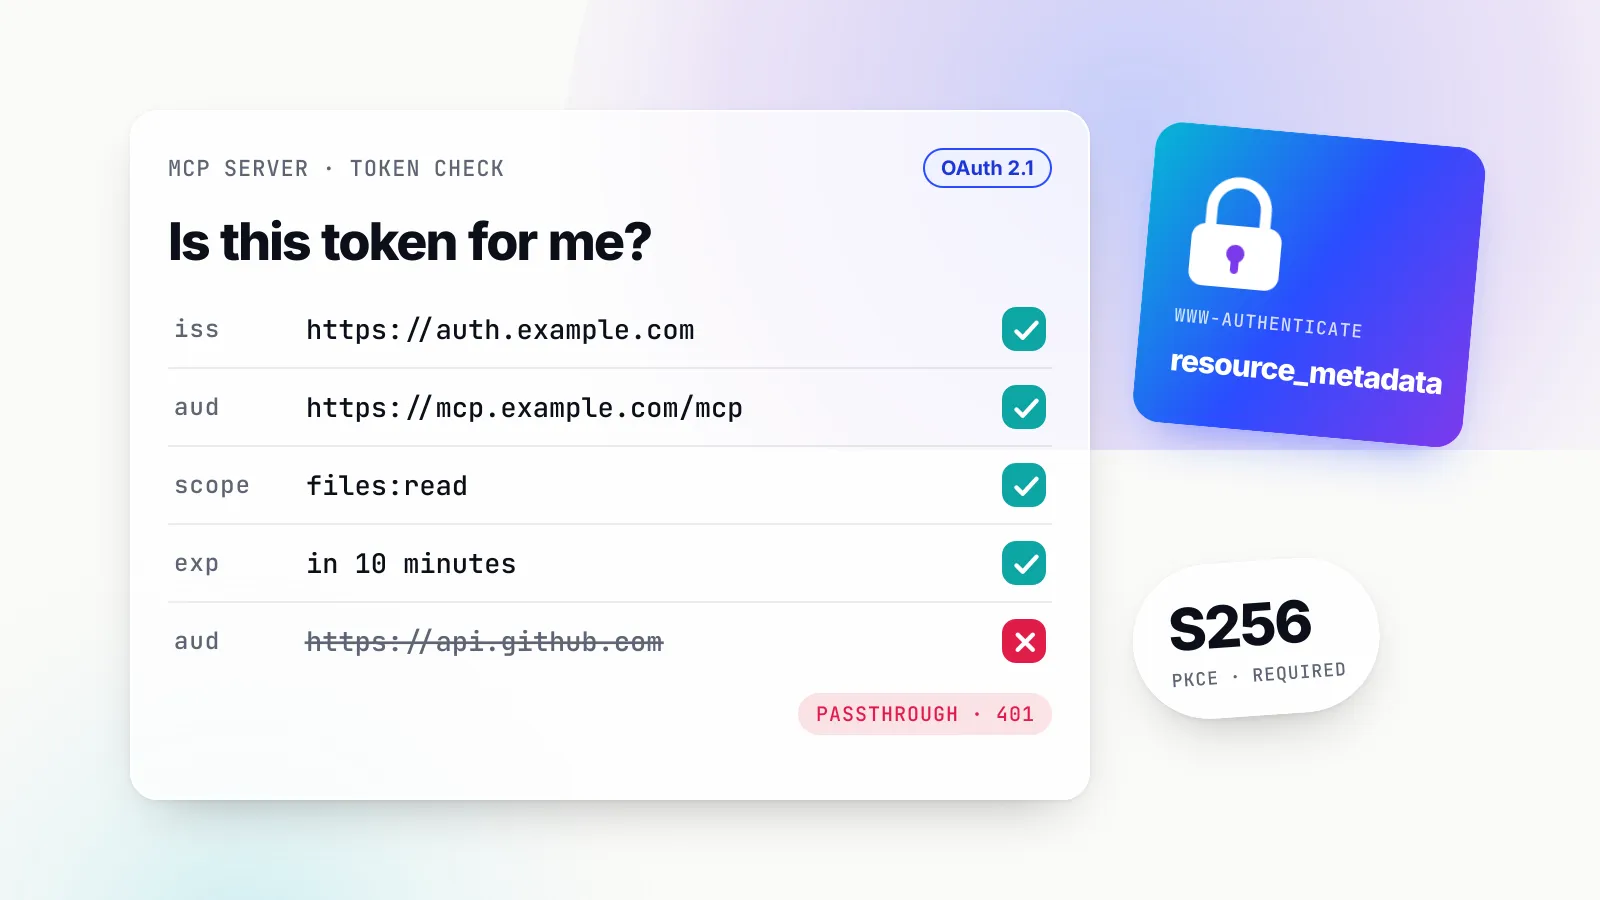
MCP security and authentication: how the OAuth flow works and where attacks land
MCP security under the 2026-07-28 spec: how OAuth 2.1 authentication works step by step, the attacks it does not stop, and a hardening checklist for teams.
ResearchExplainer
Prompt injection attacks: real examples, why they work and the defences that hold
Prompt injection examples from documented incidents, why no model has solved it, and the layered defences that cap the damage when an AI agent is fooled.